Getting a Corporate Website Built: A Step-by-Step 2026 Guide
Everything you need to know before getting a corporate website built — from setting goals and choosing an agency to preparing content and post-launch maintenance.
Read more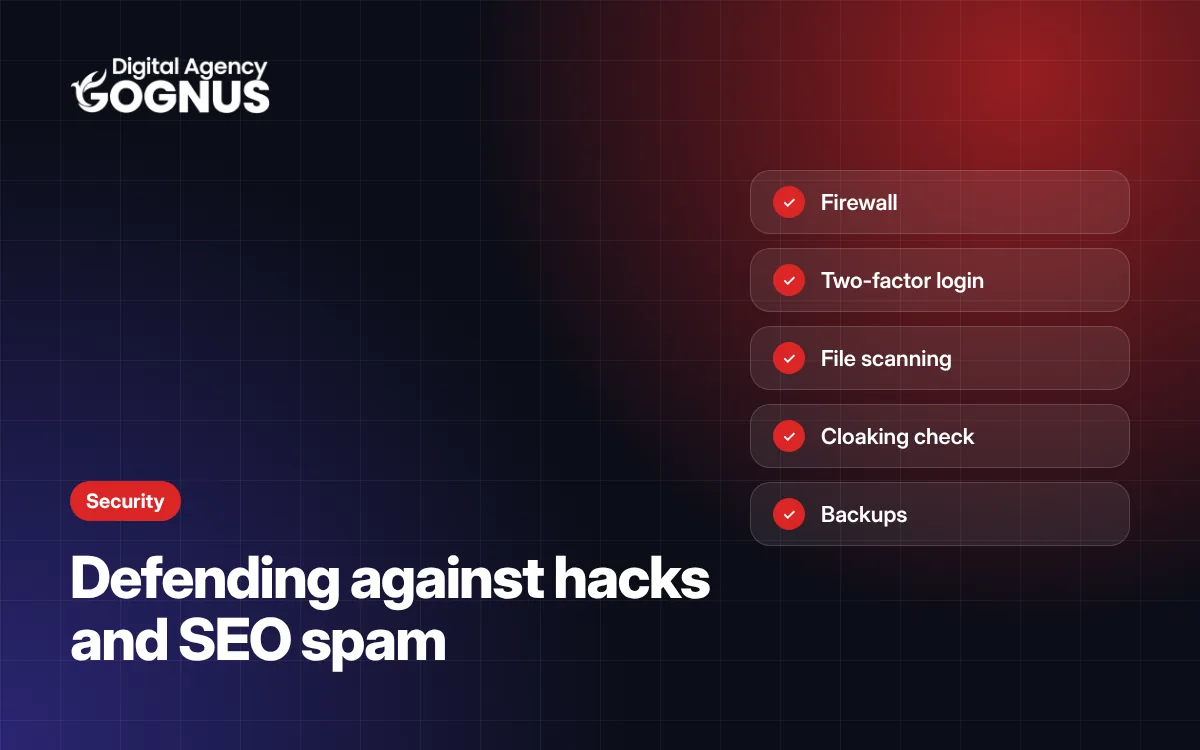
Imagine searching for your company’s name on Google one morning and seeing betting, gambling or unrelated product pages under your site’s address. This is one of the most common and most damaging consequences of a hacked site: SEO spam. In this article we explain how these attacks work, how to spot them and how to prevent them for good.
Attackers break into sites with security holes and use the site’s reputation in search engines for their own purposes. The most common methods:
site:yourcompany.com search on Google| Measure | Why it matters |
|---|---|
| Up-to-date WordPress, theme and plugins | Most attacks exploit known vulnerabilities |
| Few, trusted plugins | Every plugin is an additional attack surface |
| Strong password + two-factor authentication | A stolen password alone is not enough |
| Failed login limits | Stops brute-force attacks |
| Blocking PHP in the uploads folder | Prevents backdoor files from running |
| File integrity monitoring | Flags changed and added files immediately |
| Checking the Googlebot view | Catches cloaking early |
| Regular backups stored off-site | A quick way back in the worst case |
On the sites we deliver, a firewall, file and core integrity scanning, SEO spam and cloaking checks (detecting a different page being shown to Google), two-factor authentication, login limits, activity logging and instant email/Telegram alerts in case of anything suspicious are set up as standard. No system can promise one hundred percent protection, but spotting problems early keeps the damage to a minimum.
The most common signs are betting or unrelated product pages appearing on Google under your site’s address, a security warning in Search Console, administrator accounts you don’t recognise, visitors being redirected to other sites and the site slowing down.
Once the spam pages are removed, the site is secured and a review is requested via Search Console, visibility can recover over time; however, the time and outcome vary from site to site and cannot be guaranteed.
Not on its own. Up-to-date software, few and trusted plugins, strong passwords and two-factor authentication, regular backups, file integrity monitoring and server-level rules together provide protection.
For your site’s security and maintenance, see our hosting, maintenance and technical support service or write to us.
Field notes from our team building corporate websites, custom management panels and WordPress solutions.
Review the scope, process and what's included, or request a free quote in 2 minutes.
Everything you need to know before getting a corporate website built — from setting goals and choosing an agency to preparing content and post-launch maintenance.
Read more
Why can two corporate website quotes differ so much? We explain the 10 factors that determine the price and how to compare quotes properly.
Read more
What corporate sites that win visitors’ trust and turn them into customers have in common: a 12-point checklist.
Read more